DevSecOps Consulting – Expert Guidance at your Fingertips
Elevate your Software with Precise and Cutting-Edge DevSecOps Consultation:
Let’s Secure You from Start!
Get Started


Elevate your Software with Precise and Cutting-Edge DevSecOps Consultation:
Let’s Secure You from Start!
Software security has become an essential parameter that should get integrated with Development and Operations. Weave Security into DevOps to enhance your Software Development Lifecycle (SDLC). Automation with security is the mandate that drives software firms and business organizations. Upgrading DevOps into DevSecOps improves the performance of your organization, and we facilitate it through our cutting-edge security measures for you.
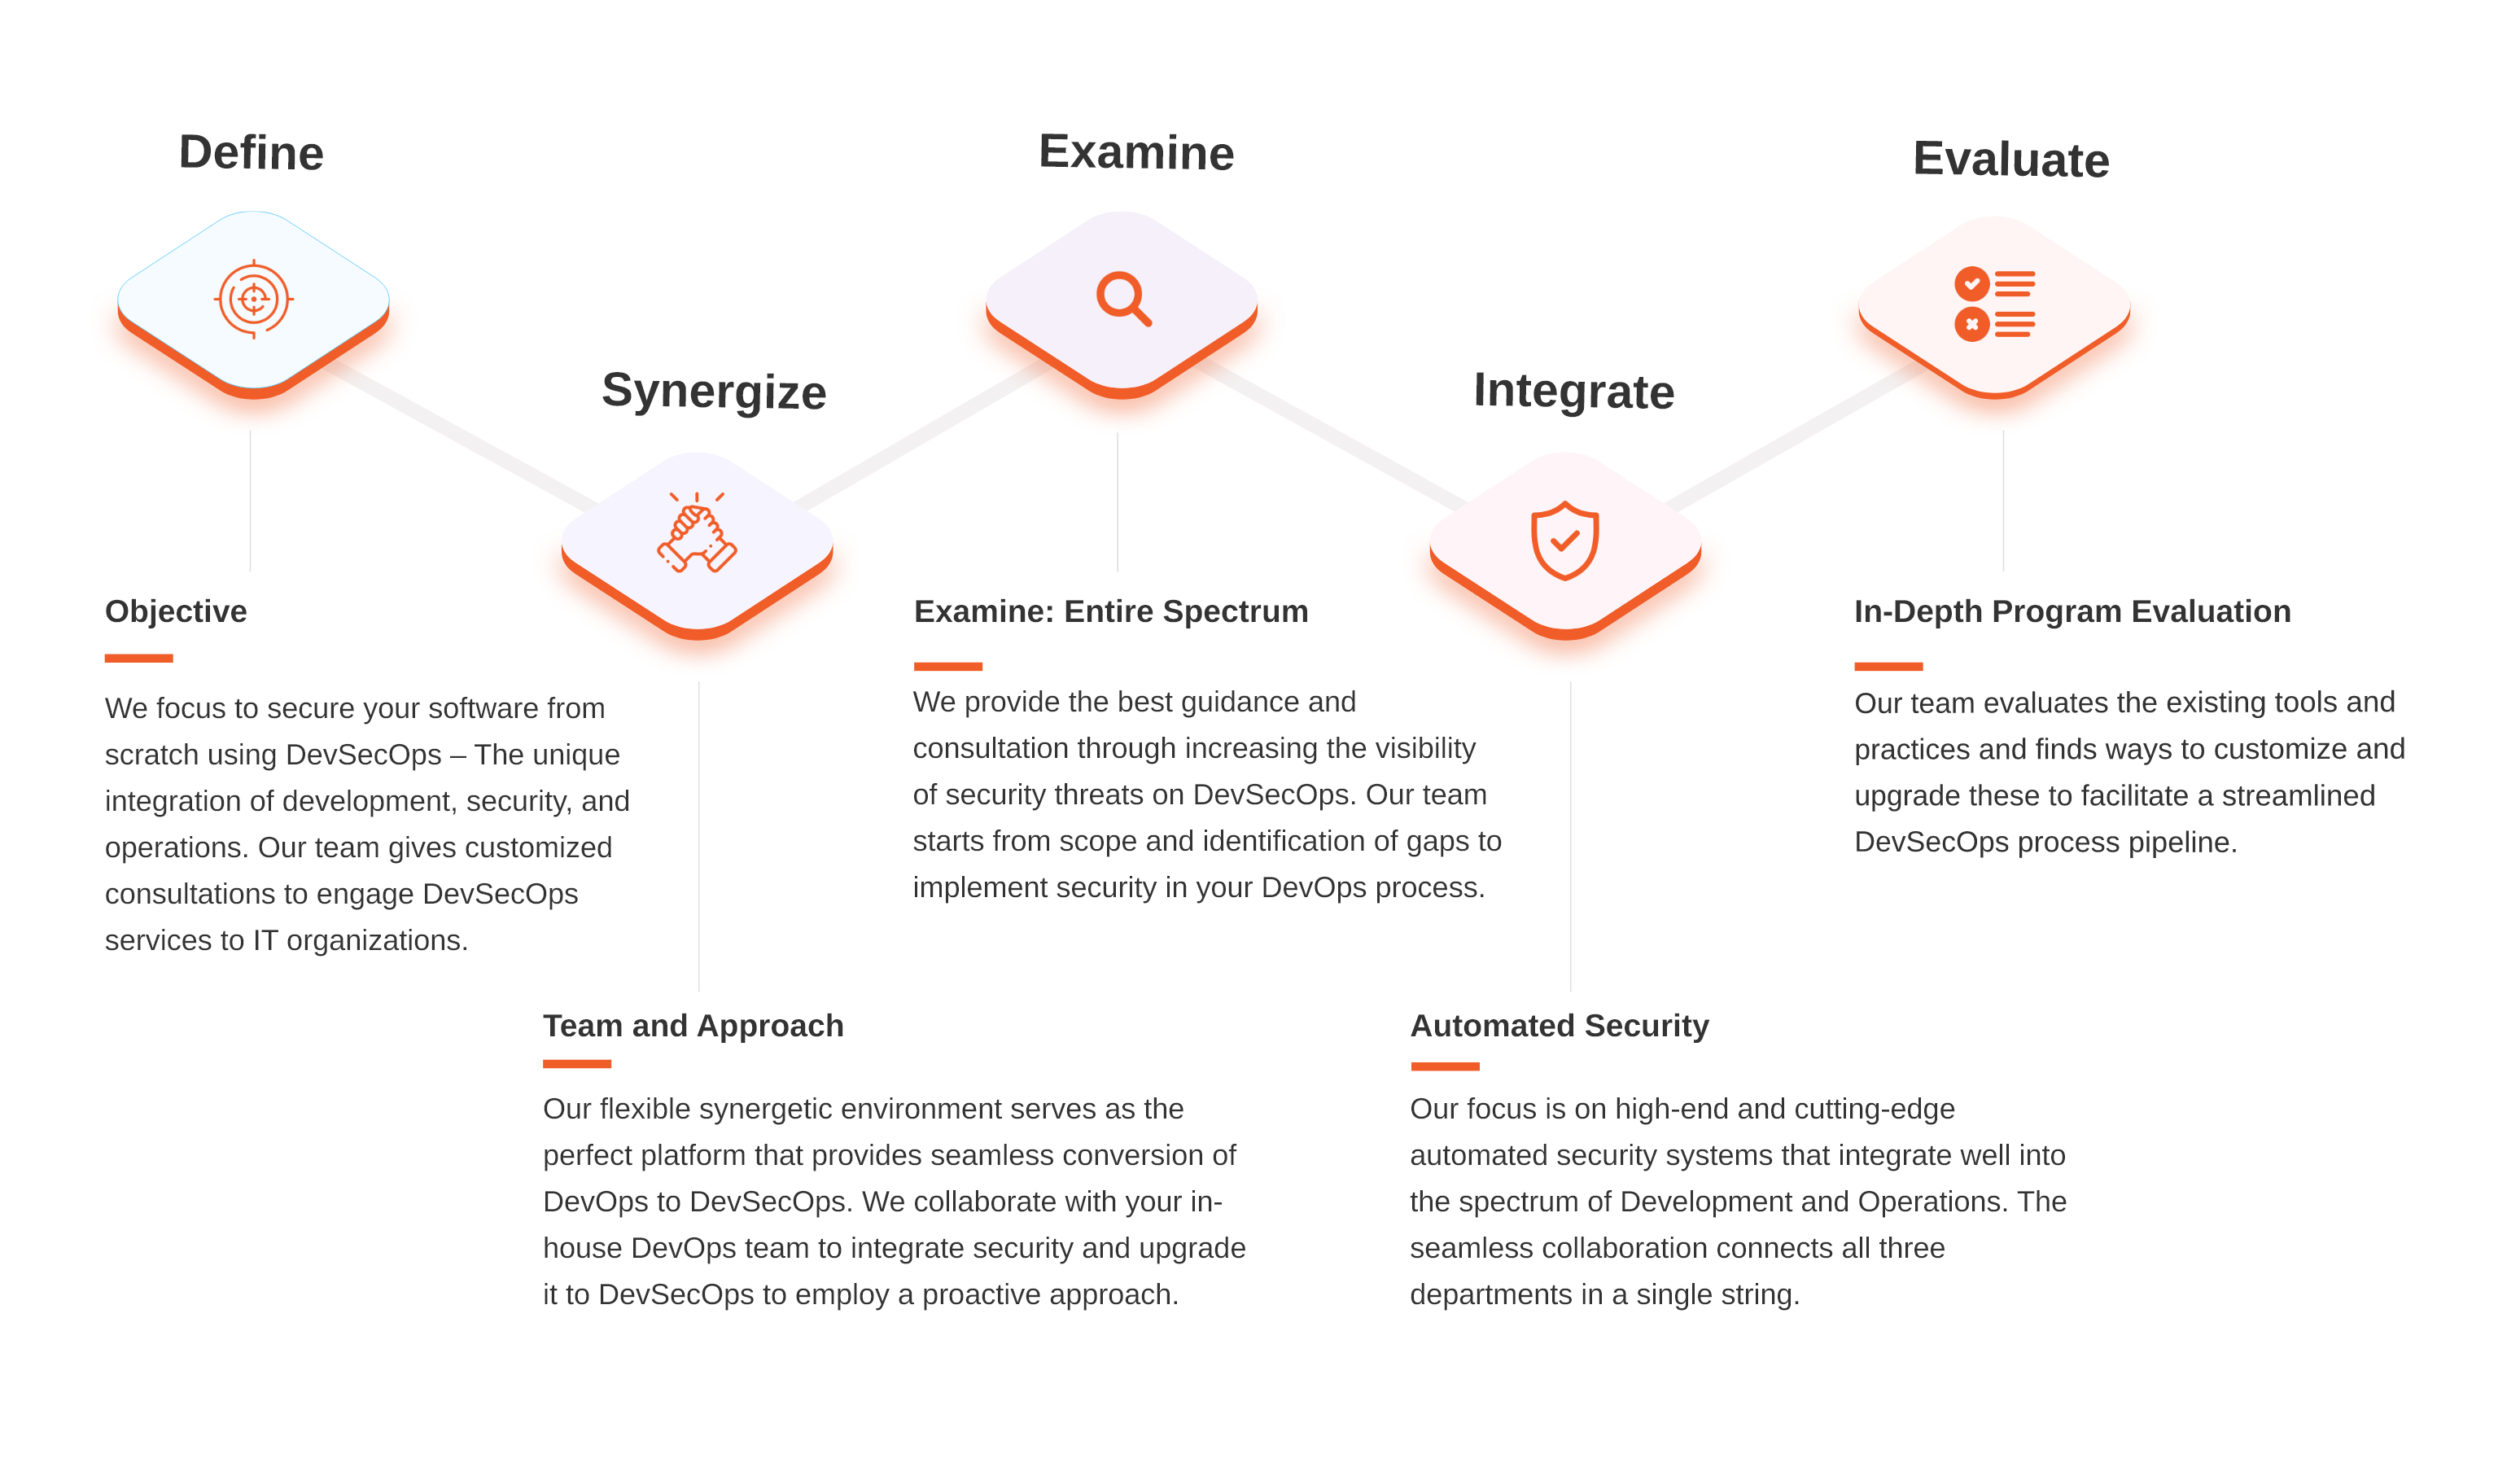
We, Urolime, form the forefront of DevSecOps consulting where you can do IT the smart way. Our experienced and expert team gives apt consultation to your DevSecOps processes.
We Guide you through all loops and hoops of DevSecOps All The Way.
We understand your infrastructure and business goals. Our team advises on how to design and implement a robust plan for DevSecOps processes.
Our experts advise you on the most suitable security technologies that can get configured and deployed at your organization.
Implement our DevSecOps process with cloud-based security technologies to unlock advanced threat detection, threat intelligence, and vulnerability scanning to be audit-ready.
We help you with detailed documentation and build in-house knowledge to monitor system performance and functions for managing the infrastructure like a pro.
Our team assists your engineers and teams at every phase of DevSecOps processes

170 in-house engineers, including CKS, CKA & Certified Kubernetes Application Developers.

DevSecOps best practices we've mastered while collaborating with over 100+ clients

Team up with an experienced Kubernetes service provider.

Experience navigating the transition from cloud solutions to large-scale IT delivery

Collaborate with our team of CNCF Certified Professionals, ensuring solid expertise and reliable solutions for your projects.

Effortlessly expand your team of engineers without the burdens of recruitment or training.
DevSecOps builds on DevOps by embedding security into every stage of the pipeline, instead of treating it as a final gate.
| Factor | DevSecOps | Traditional DevOps |
|---|---|---|
| Security integration | Built into every pipeline stage | Often a separate, later-stage review |
| Vulnerability detection | Continuous scanning (IAST, SAST, DAST) | Periodic or pre-release testing |
| Compliance readiness | Ongoing audit-readiness built in | Addressed closer to release or audit |
| Incident response | Automated remediation and threat detection | Manual response after issues surface |
| Team ownership | Shared across Dev, Sec, and Ops | Security often owned by a separate team |
Assessment of existing DevOps processes, a customized DevSecOps roadmap and migration strategy, integration of security into the CI/CD pipeline, vulnerability scanning (IAST, SAST, DAST), container and package security analysis, threat modeling, and managed DevSecOps services.
Traditional DevOps focuses on collaboration between development and operations to speed up delivery. DevSecOps builds security into every stage of that pipeline, from code commit through deployment, rather than treating it as a separate step at the end.
Yes. Urolime's DevSecOps services help organizations become compliant and audit-ready against regulations including HIPAA, GDPR, and PCI DSS.
Yes. Urolime has experience securing both bare-metal and managed Kubernetes environments, including AWS EKS, GKE, and AKS, as part of a DevSecOps engagement.
Yes. Urolime offers end-to-end managed DevSecOps services, handling threat prevention through mitigation and providing documentation to help your team maintain the processes going forward.
© 2026 All rights reserved Urolime Technologies


